Skip to content
IonWarpTry for free

SAST tool

The SAST tool that reads your pull requests like an attacker.

Pattern rules flag a line. IonWarp's Security Review follows the change through your code and names who could abuse it and what they would get: a tenant leak, an injected command, a secret sent to a model. It lands in the same GitHub comment as Code Review, with a fix prompt for your coding agent.

discourse-graphite#4
Enhance embed URL handling and validation system
app/controllers/embed_controller.rbdiscourse-graphite #4
IonWarp caught it Qodo, Greptile, CodeRabbit and Cursor Bugbot missed it
IonWarpbotcommented on line 26

P2Embed endpoint's only gate is the caller-supplied Referer header · Security Review

GET /embed/best is unauthenticated and its sole control against third-party embedding is `URI(request.referer).host != SiteSetting.embeddable_host`. Referer is a request header a client sets freely, so any HTTP client (or a script running on the embeddable host) can send `Referer: http://<embeddable_host>/` and still get the embed page with `X-Frame-Options: ALLOWALL`, defeating the single-host restriction. The embed_url query parameter itself is never validated against the allowed host on this read path (only the background retrieval validates it), so any existing TopicEmbed row is reachable even if its URL is on a feed-provided host.

MediumKnown issue in the Security Review benchmark · caught by DeepSeek V4.1 FlashSee the graded case

  • Starter is free for 3 people
  • One team price: Pro is $49/mo for 5 seats
  • Read-only code access
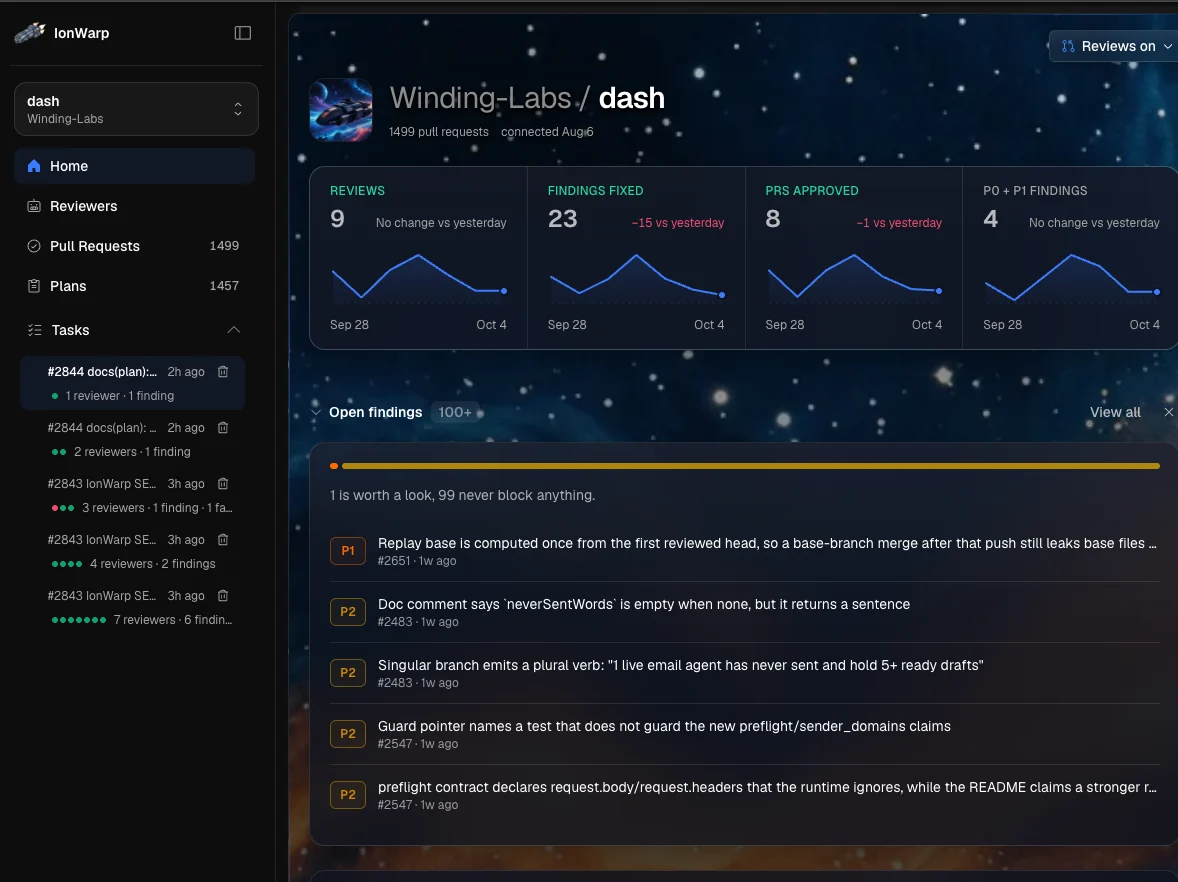
An IonWarp workspace home: reviews, findings fixed, pull requests approved and P0/P1 findings by day, then the open findings by severity.
52security P0/P1 findings fixedIonWarp's own pull requests, Aug 27 – Nov 2
$0.04model cost of one reviewAI Architecture · DeepSeek V4.1 Flash · 58 s

Security findings from IonWarp's own pull requests

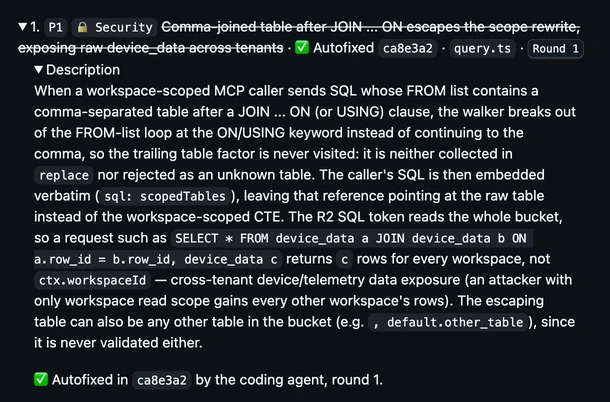
A P1 security finding on one of IonWarp's own pull requests: a comma-joined table after JOIN … ON escapes the workspace scope rewrite, so one workspace's read key reads every workspace's device data — autofixed in round 1.

Catches the query that reads every customer's rows

A comma-joined table after a JOIN slipped past a workspace scope rewrite, so a key that could read one workspace could read every workspace's device data. The finding named the query, who could abuse it and what they would get; the coding agent fixed it in round 1.

Try for free
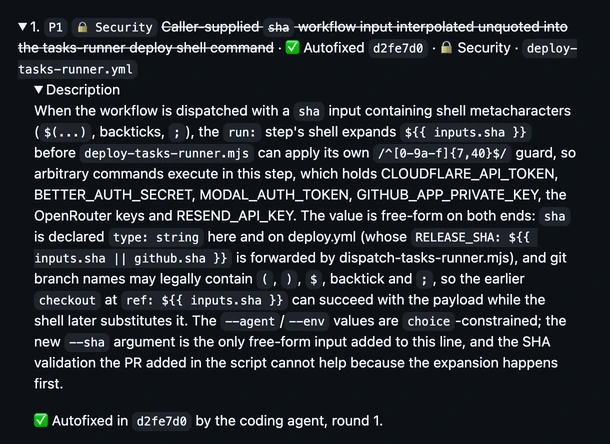
A P1 security finding on one of IonWarp's own pull requests: a caller-supplied workflow input is put unquoted into a shell command in a step that holds the deploy keys — autofixed in round 1.

Finds the input that reaches a shell

A deploy workflow put a caller's `sha` input into a shell command unquoted, in a step that holds the deploy keys. The finding showed why the script's own check came too late: the shell expands the input first.

Try for free
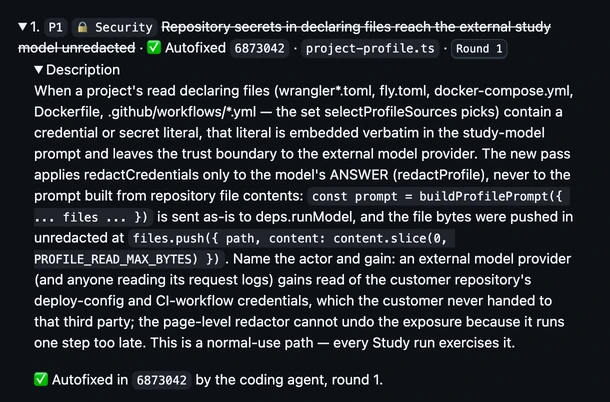
A P1 security finding on one of IonWarp's own pull requests: credentials in a repository's deploy config files are copied unredacted into a prompt for an outside model — autofixed in round 1.

Sees a secret leave through a prompt

A new pass read a repository's deploy config files into a prompt for an outside model and redacted only the answer, so any credential in those files went to the model provider. A pattern scanner has no rule for that; the fix moved redaction before the prompt.

Try for free
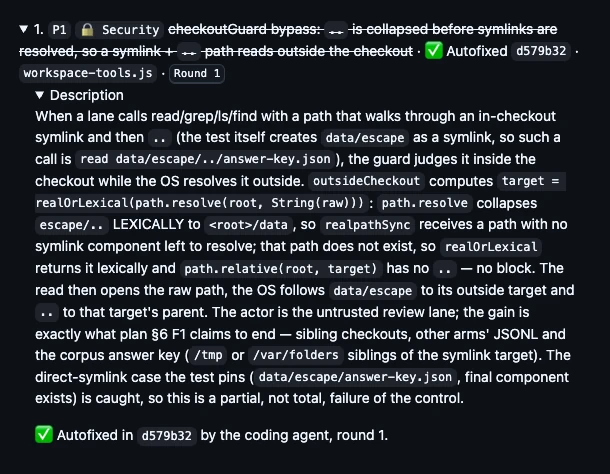
A P1 from Security Review: a path guard collapses `..` before resolving symlinks, so a symlink plus `..` reads outside the checkout — autofixed in round 1.

Names the path an attacker would take

A path guard collapsed `..` before it resolved symlinks, so a symlink could read files outside the checkout. Security Review named the path and how to close it.

Try for free
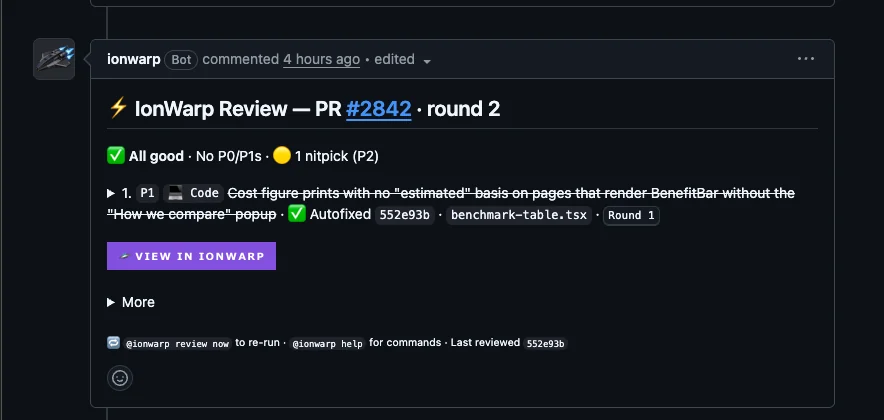
An IonWarp review comment in round 2: no P0 or P1 left, and a round-1 P1 struck through and marked Autofixed with its commit.

Your agent closes it; IonWarp checks the fix

Every finding carries a fix prompt for Claude Code, Cursor or Codex. The GitHub App only reads your code, so it never pushes: your agent pushes the fix, and IonWarp re-reviews and strikes the finding through as Autofixed, or keeps it open.

Try for free
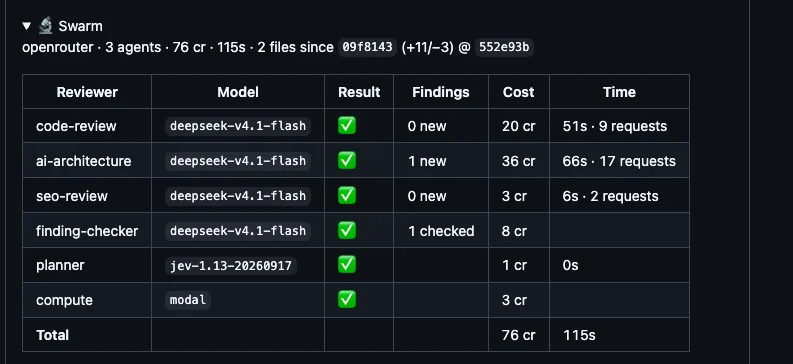
The reviewer table in an IonWarp pull-request comment: three reviewers on DeepSeek V4.1 Flash, the finding checker and the planner, with each one's cost and time — 76 credits and 115 s in all.

Each reviewer's model, cost and time

Every review comment ends with a table of the reviewers that ran: the model each used, what it found, what it cost and how long it took. The review shown took 115 s and 76 credits.

Try for free

IonWarp and the SAST tools teams compare it with

Save 60% vs SnykIonWarp$49/moSnyk$125/moSemgrep$225/moGitHub Advanced Security$245/moAikido$350/mo
Reviews pull requests for securitySecurity Review joins the pull requests that touch auth, input, data access or secretsPass/fail pull request checks; inline comments on up to 10 Snyk Code issues[1][2]PR and MR comments, on every plan[3][4]Dependency review and AI Scan during pull request review[5]PR checks and inline comments from Basic up; not on Free[6][7]
Says how an attacker would use itEach finding names the actor, the path and what they gainNot listedNot listedNot listedNot listed
Finds leaked secretsIn the pull request: keys in code, prompts, client bundles and logs — not git historySnyk Secrets, generally available Aug 2026; the plans page prices it on Enterprise credits[8][9]Semgrep Secrets, $15 per contributor; not on Free[3]Secret scanning, and push protection that blocks commits with secrets[5]Secrets detection, on every plan[6]
Scans a whole branchA full-branch security audit you start from the appTests each imported project: 100 Snyk Code tests a month on Free, 1,000 on Team[9]Full scans; Free covers up to 10 repositories[3]Code scanning, in Code Security[5]10 repositories on Free, 100 on Basic[6]
Known-vulnerable dependenciesNo CVE database: keep GitHub's Dependabot for packagesSnyk Open Source, on every plan[9]Supply Chain, free for up to 10 contributors[3]Dependabot security updates, free on every plan[10]Dependency scanning, on every plan[6]
How a finding gets fixedYour coding agent fixes it from the finding's prompt; IonWarp re-checks the pushOpens a fix pull request for each new actionable vulnerability[11]Autofix, on every plan[3]Copilot Autofix suggests fixes for code scanning alerts[5]AutoFix pull requests: 10 a month on Free, unlimited from Basic[6][12]
Code review in the same appCode Review on each pull request, in one comment with the security findingsNot listedNot listedNot listedPR code quality checks from Basic up[6]
Free planStarter: free for 3 peopleFree: 5 projects, 100 Snyk Code tests a month[9]Code and Supply Chain free for up to 10 contributors and 10 repositories[3]Public repositories only: secret scanning, push protection, Copilot Autofix[10]Free for 2 users and 10 repositories[6]
What 5 developers pay a month$49/mo for 5 developers — one Pro workspace with 5 seats included.$125/mo for 5 developers — Team at $25 each, 5-developer minimum, billed monthly.[13]$225/mo for 5 developers — Teams, Code + Secrets at $45 each, $30 for Code plus $15 for Secrets.[3]$245/mo for 5 developers — Code Security + Secret Protection at $49 each, per active committer, on a GitHub Team or Enterprise plan.[10]$350/mo on Basic, a flat fee that includes 10 users (US pricing).[6]
Git platformsGitHub, and GitHub Enterprise on EnterpriseGitHub, GitLab, Bitbucket and Azure Repos.[14]GitHub, GitLab, Bitbucket and Azure DevOps.[4]GitHub.[5]GitHub, GitLab, Bitbucket and Azure DevOps.[7]

Competitor facts are from each vendor's own pages, dated in the sources below. “Not listed” means the vendor's pages name no such feature; prices are for 5 developers on the team plan each price cell names.

Sources

  1. Pull Request checksSnyk docs · read
  2. Pull Request experienceSnyk docs · read
  3. Pricing and PlansSemgrep · read
  4. Supported source code managersSemgrep docs · read
  5. About GitHub Advanced SecurityGitHub Docs · read
  6. PricingAikido Security · read
  7. AutoFix Suggestions and Inline Commenting for PR ChecksAikido help · read
  8. Snyk Secrets Now Generally AvailableSnyk · read
  9. Snyk Plans and PricingSnyk · read
  10. GitHub Advanced Security plansGitHub · read
  11. Enable automatic Fix PRsSnyk docs · read
  12. Automatic Creation of Pull RequestsAikido help · read
  13. Get started with your Snyk Team planSnyk · read
  14. SCMsSnyk docs · read

Put a security reviewer on your next pull request

Install the GitHub App and pick your repositories. Your next pull request gets a review comment.

Starter is free for 3 people · Pro is $49/mo for 5 seats

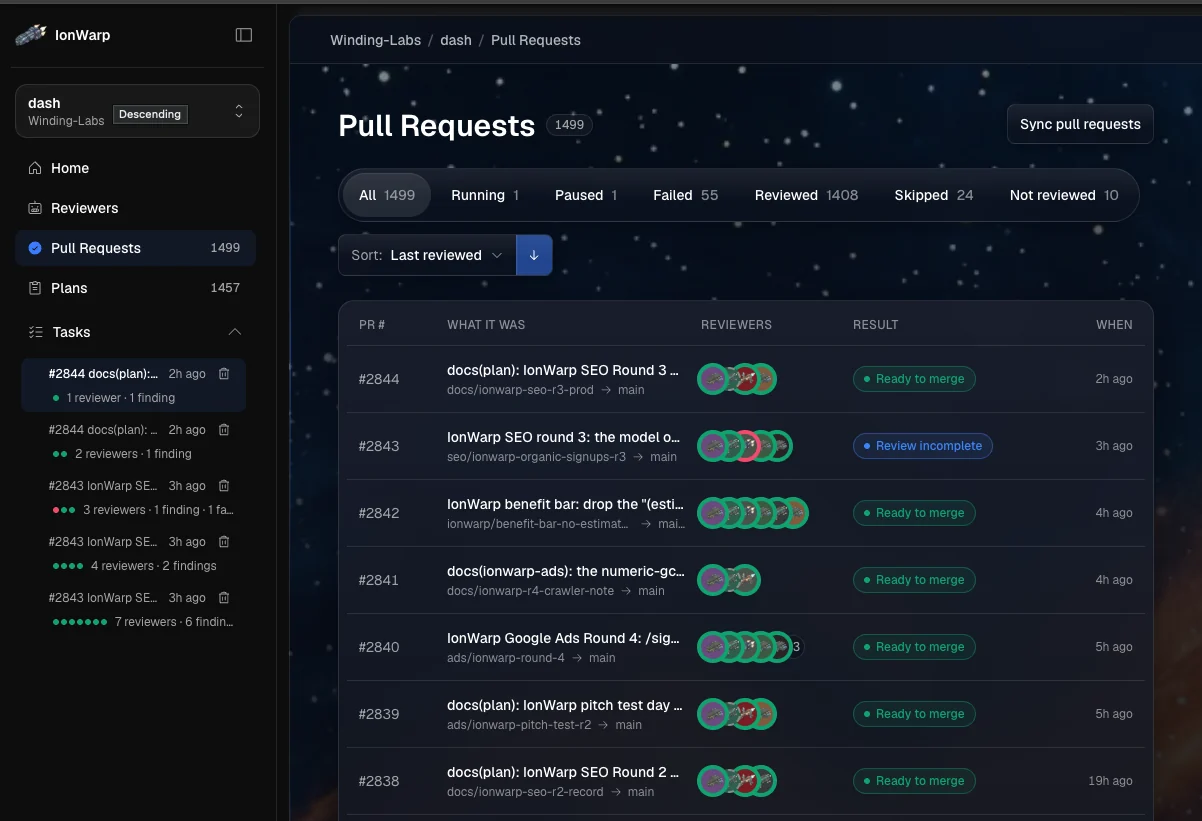
IonWarp's Pull Requests page for its own repository: 1,499 pull requests, each row with the reviewers that ran on it and its result.