 IonWarp
 IonWarp
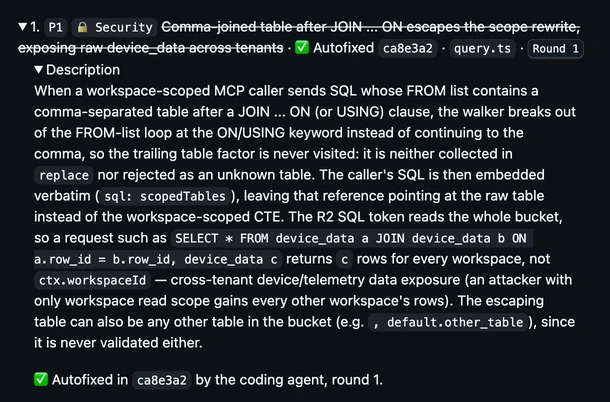
Catches the change that shows one customer another's data
A comma-joined table after a JOIN slipped past a workspace scope rewrite, so a key that could read one workspace could read every workspace's device data. The finding named the query, who could abuse it and what they would get; the coding agent fixed it in round 1.


P2Embed endpoint's only gate is the caller-supplied Referer header · Security Review
GET /embed/best is unauthenticated and its sole control against third-party embedding is `URI(request.referer).host != SiteSetting.embeddable_host`. Referer is a request header a client sets freely, so any HTTP client (or a script running on the embeddable host) can send `Referer: http://<embeddable_host>/` and still get the embed page with `X-Frame-Options: ALLOWALL`, defeating the single-host restriction. The embed_url query parameter itself is never validated against the allowed host on this read path (only the background retrieval validates it), so any existing TopicEmbed row is reachable even if its URL is on a feed-provided host.