The Snyk alternative for teams whose risk is in their own code.
Snyk prices each developer; IonWarp prices the team. It reviews the code your team and its agents write — a missing tenant check, an unquoted input, a key sent to a model — on the pull requests that need it, with Code Review on each one. Keep GitHub's free Dependabot for your packages.
IonWarp caught it Qodo, Greptile, CodeRabbit and Cursor Bugbot missed it
IonWarpbotcommented on line 26
P2Embed endpoint's only gate is the caller-supplied Referer header · Security Review
GET /embed/best is unauthenticated and its sole control against third-party embedding is `URI(request.referer).host != SiteSetting.embeddable_host`. Referer is a request header a client sets freely, so any HTTP client (or a script running on the embeddable host) can send `Referer: http://<embeddable_host>/` and still get the embed page with `X-Frame-Options: ALLOWALL`, defeating the single-host restriction. The embed_url query parameter itself is never validated against the allowed host on this read path (only the background retrieval validates it), so any existing TopicEmbed row is reachable even if its URL is on a feed-provided host.
MediumKnown issue in the Security Review benchmark · caught by DeepSeek V4.1 FlashSee the graded case
You start on Starter: about 70 reviews
One team price: Pro is $49/mo for 5 seats
Read-only code access
ionwarp.com
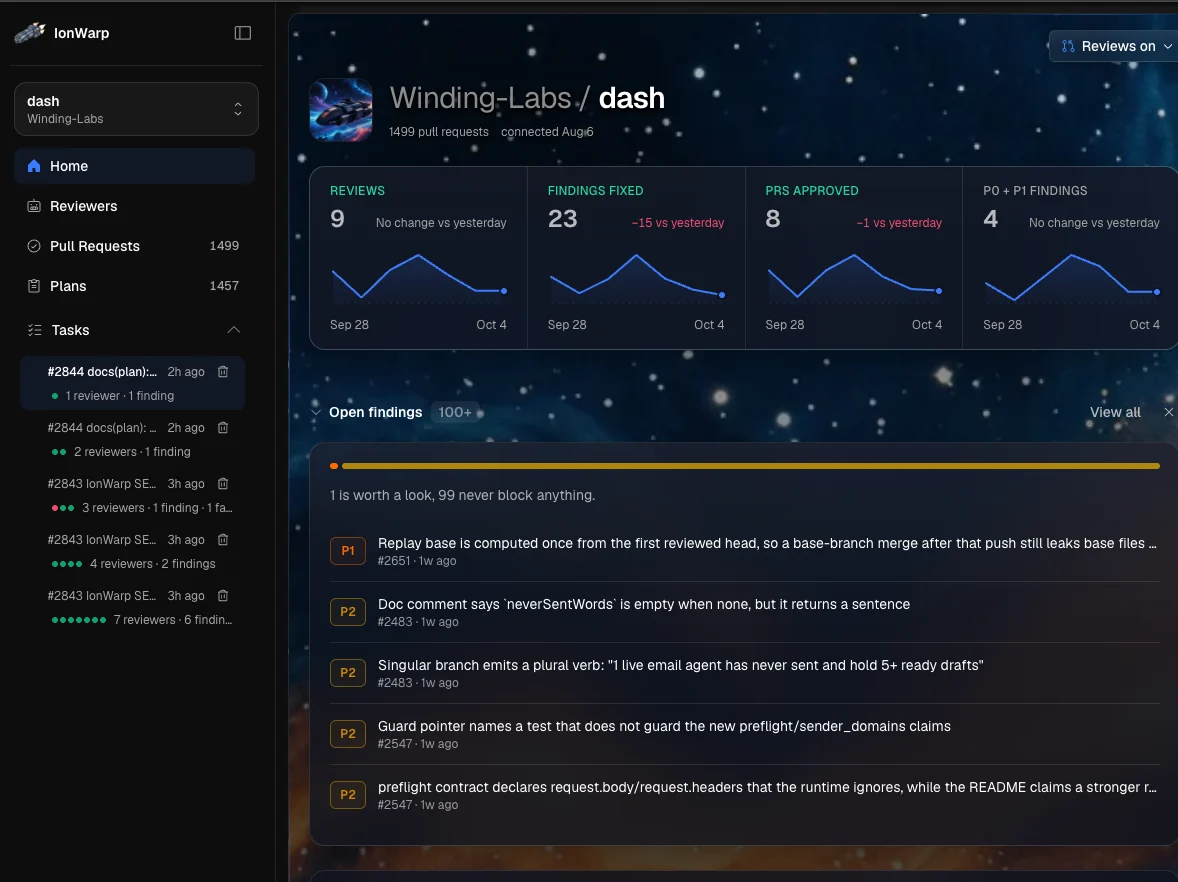
52security P0/P1 findings fixedIonWarp's own pull requests, Aug 27 – Nov 2
$0.04model cost of one reviewAI Architecture · DeepSeek V4.1 Flash · 58 s
What it caught in IonWarp's own code
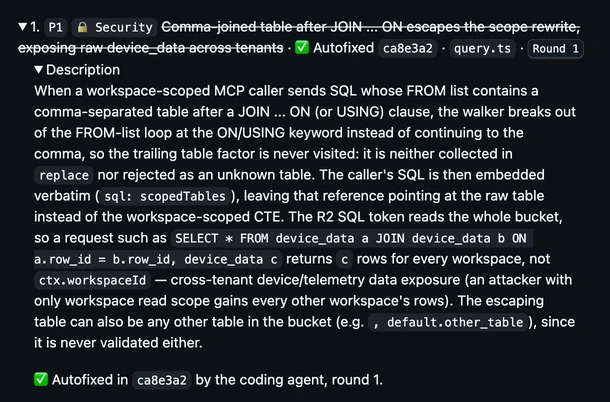
Catches the query that reads every customer's rows
A comma-joined table after a JOIN slipped past a workspace scope rewrite, so a key that could read one workspace could read every workspace's device data. The finding named the query, who could abuse it and what they would get; the coding agent fixed it in round 1.
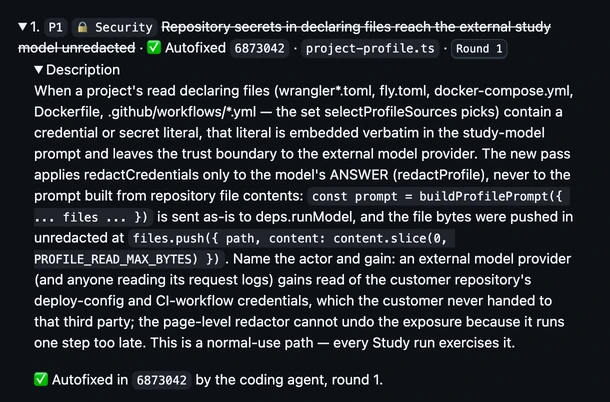
Sees a secret leave through a prompt
A new pass read a repository's deploy config files into a prompt for an outside model and redacted only the answer, so any credential in those files went to the model provider. A pattern scanner has no rule for that; the fix moved redaction before the prompt.
Finds the input that reaches a shell
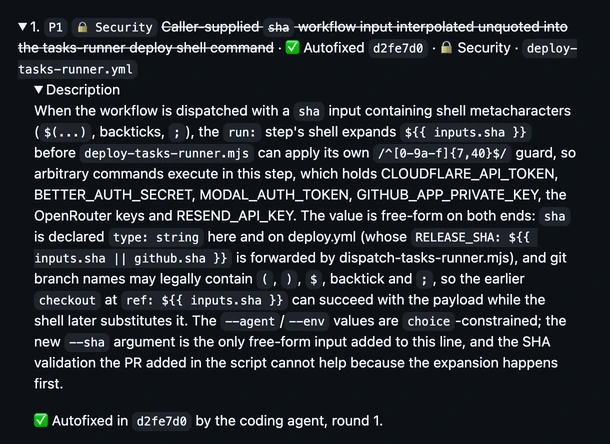
A deploy workflow put a caller's `sha` input into a shell command unquoted, in a step that holds the deploy keys. The finding showed why the script's own check came too late: the shell expands the input first.
Specialists join when the diff needs them
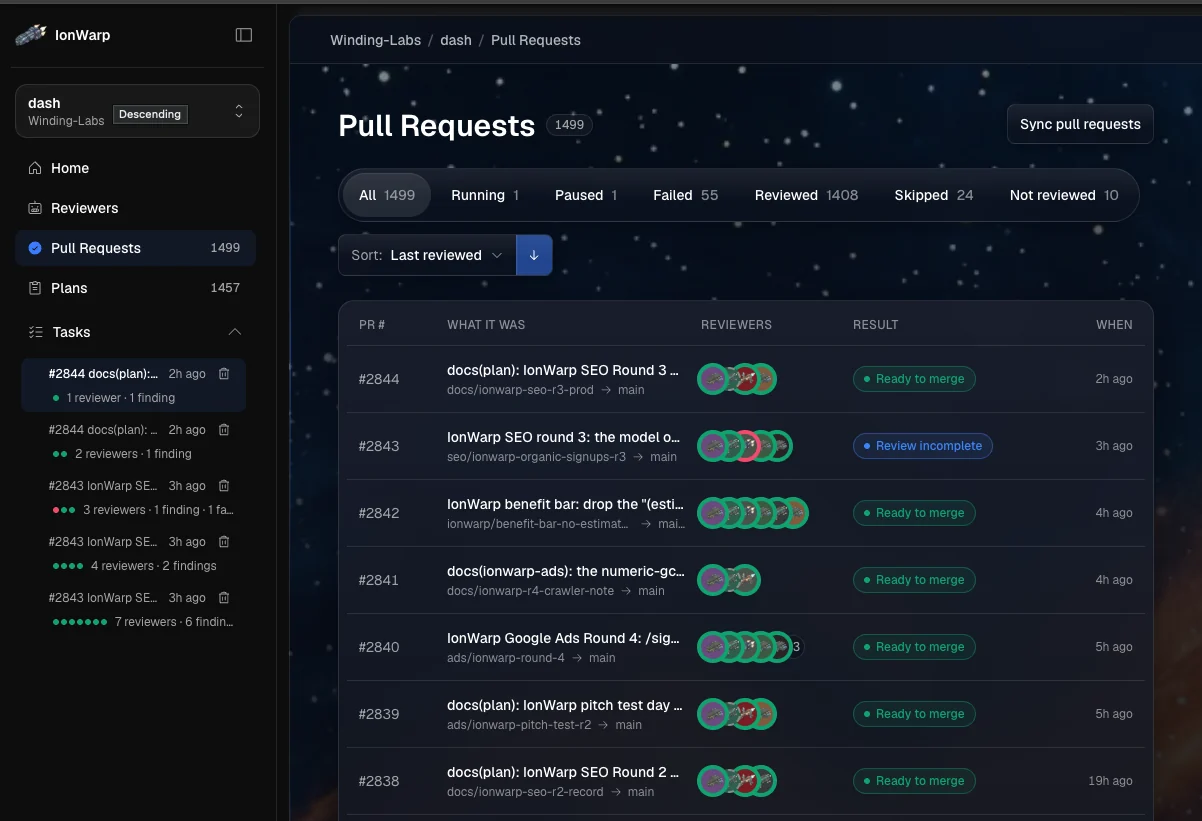
A planner reads each pull request and adds the reviewers it needs beside Code Review: security, architecture, performance, docs, SEO, analytics or UX. Each runs on the plans shown.
16 reviewers in the catalog
One GitHub comment for all of them
Each reviewer's findings are labeled with its name
Code ReviewEvery plan
Security ReviewEvery plan
AI ArchitecturePro
API PerformanceMax
Docs ReviewPro
SEO ReviewMax
Analytics ReviewMax
UX ReviewMax
Your agent closes it; IonWarp checks the fix
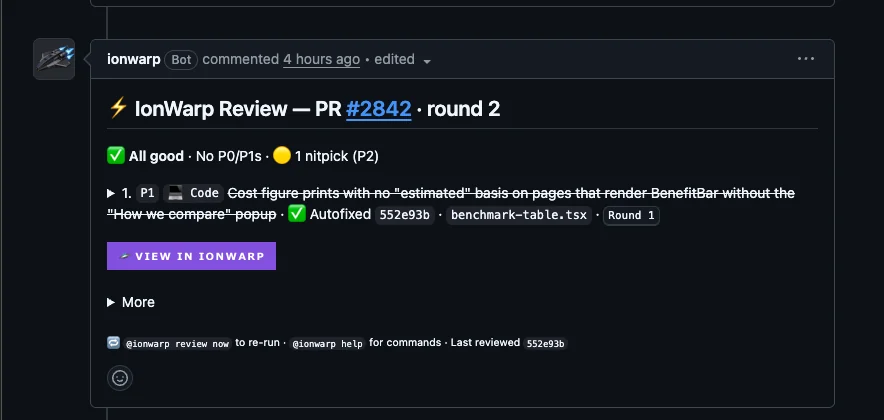
Every finding carries a fix prompt for Claude Code, Cursor or Codex. The GitHub App only reads your code, so it never pushes: your agent pushes the fix, and IonWarp re-reviews and strikes the finding through as Autofixed, or keeps it open.
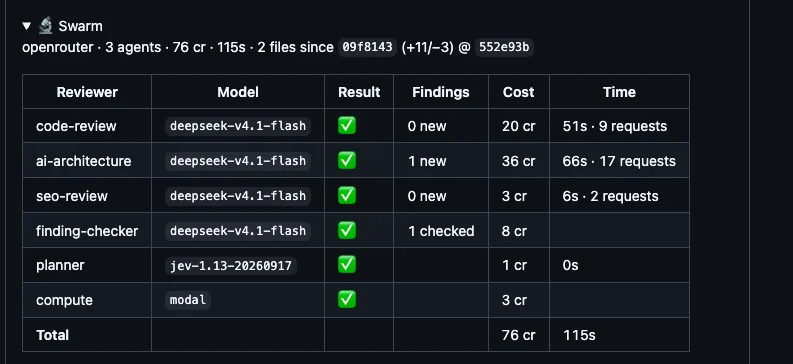
Each reviewer's model, cost and time
Every review comment ends with a table of the reviewers that ran: the model each used, what it found, what it cost and how long it took. The review shown took 115 s and 76 credits.
IonWarp, Snyk and the rest of a Snyk shortlist
Save 60% vs SnykIonWarp$49/mo
Snyk$125/mo
Aikido$350/mo
Semgrep$225/mo
GitHub Advanced Security$245/mo
Reviews pull requests for security
Security Review joins the pull requests that touch auth, input, data access or secrets
Pass/fail pull request checks; inline comments on up to 10 Snyk Code issues[1][2]
PR checks and inline comments from Basic up; not on Free[3][4]
Competitor facts are from each vendor's own pages, dated in the sources below. “Not listed” means the vendor's pages name no such feature; prices are for 5 developers on the team plan each price cell names.
 IonWarp
 IonWarp


P2Embed endpoint's only gate is the caller-supplied Referer header · Security Review
GET /embed/best is unauthenticated and its sole control against third-party embedding is `URI(request.referer).host != SiteSetting.embeddable_host`. Referer is a request header a client sets freely, so any HTTP client (or a script running on the embeddable host) can send `Referer: http://<embeddable_host>/` and still get the embed page with `X-Frame-Options: ALLOWALL`, defeating the single-host restriction. The embed_url query parameter itself is never validated against the allowed host on this read path (only the background retrieval validates it), so any existing TopicEmbed row is reachable even if its URL is on a feed-provided host.